SSL Certificate help
Fellow Sajha friends I am in the process of developing Facebook apps for client(s) that runs on iFrame. Since last October, Facebook requires a secure connection to run app. Not sure how to handle this situation as our entire clients website run on same server. This app will be used by only few clients. I did some Google about the SSL certificate types. Looks like multi-domain Certificate might work (Not sure though). What kind of setup is required on Load balancer? And also I think I need to reconfigure the IIS on webserver to support secure request. Please suggest. There is a single website setup on IIS. Based on the URL requested, the code pulls the settings from the database and displays website. For example, if the request is domain1.com, the code will pull only setting for domain1 and displays the content on domain1.com. If the request URL is domain2.com, it pulls the setting only for domain2 and displays the content on domain2.com domain1.com/ social/facebookapp domain2.com/social/facebookapp Any suggestions will be highly appreciated. Thank you Last edited: 17-Jul-12 03:08 PM
mukurdhom · Jul 17, 2012 10:30 AM · 14,167 views
@mukurdhom, Load balancers typically have SSL termination capability, and can have wildcard certs configured directly on them. If your LBs don't have SSL support, you can submit individual certificate requests to a CA (Certificate Authority) for each subdomain/server -- which may add management burden and possibly cost more, in comparison to adding SSL termination support to the LBs. Since your infrastructure already has a load balancer, I'd look into applying an wildcard cert, and call it a day! Not sure what LB product your firm uses, the concept and process outlined below are pretty standard across the board: http://support.f5.com/kb/en-us... Hope this helps! ~@~ Last edited: 17-Jul-12 11:13 AM
saajha · Jul 17, 2012 11:06 AM
@ Mukurdhom , Since your diagram shows domain1 , domain2 etc.. , wild card certificate would not work , however multi-domain ssl certificate would work. Or in another case, you would have to get SSL Cert for individual domain and since they seem to be hosted on the same webservers , you would have to use multiple IPs on the web servers for each website. It's a little more complicated to support different SSL Certificates on the same IP. Thanks Nishant
nishant322 · Jul 19, 2012 1:02 PM
If those are separate domains -- then wildcard cert is indeed not the solution. My impression, from "There is a single website setup on IIS.." is that there's a single domain (with multiple subdomains) associated with the site. If there's a way to get the client(s) trust self-signed certs, you could establish your own certificate authority, and generate certificates. It's mostly feasible in a proxy'd environment, as you only need to make the proxy trust that cert, and have the trust inherit down to the browsers. ~@~
saajha · Jul 19, 2012 3:54 PM
I don't know so much about how it is done through load balancers but you can give a try to the following: 1. Install the certificates to the "Local Computer". 2. Import the certificates to the IIS. 3. Assign www.domain1.com certificate to the www.domain1.com website. 4. Require IIS to have secure connection. If you tell me the OS and IIS version, i might be able to give a more detailed response. The load balancers have a lot of capabilities. This might be also done easily from the load balancer.
jhapaliketo · Jul 19, 2012 6:36 PM
This conversation is preserved exactly as it was on the original Sajha.com and can't accept new replies.
Start a New DiscussionYou might be interested in...


-
Room Available for Rent USD 850.00Melrose, MA ·
-
One bed room available for rent USD 1,300.00Germantown, MD ·
-
Malden, MA, United States · Reposted Originally posted
-
Big Room with Parking Next to bus stop USD 1,100.00Everett, MA ·
-
Rooms Available for Rent USD 2,700.00Reston, VA ·
-
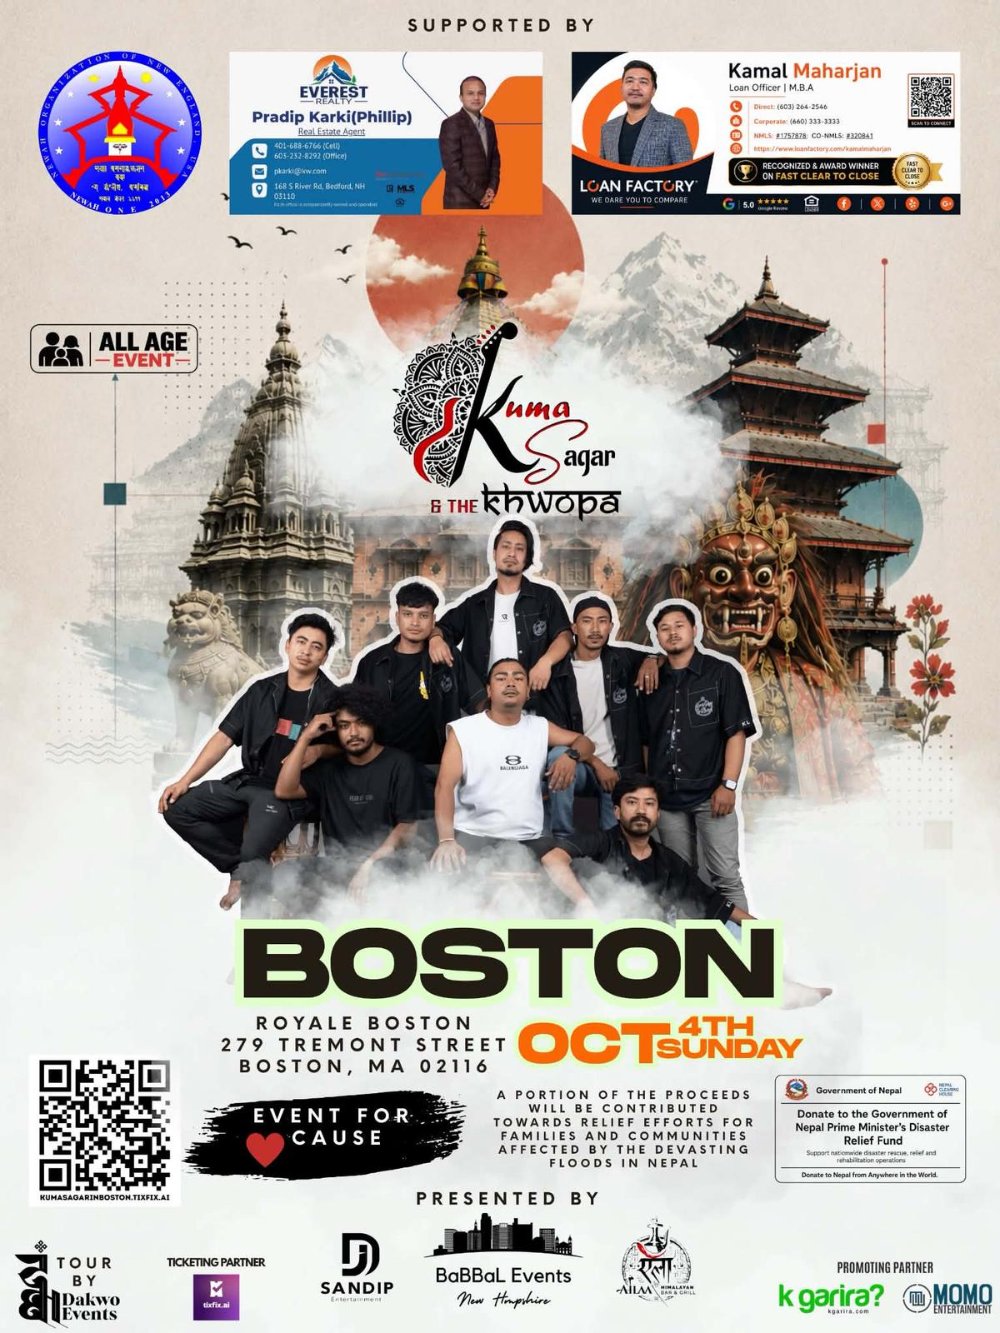 Oct 4, 2026 7:00 PM · Boston / New England · 507 views
-
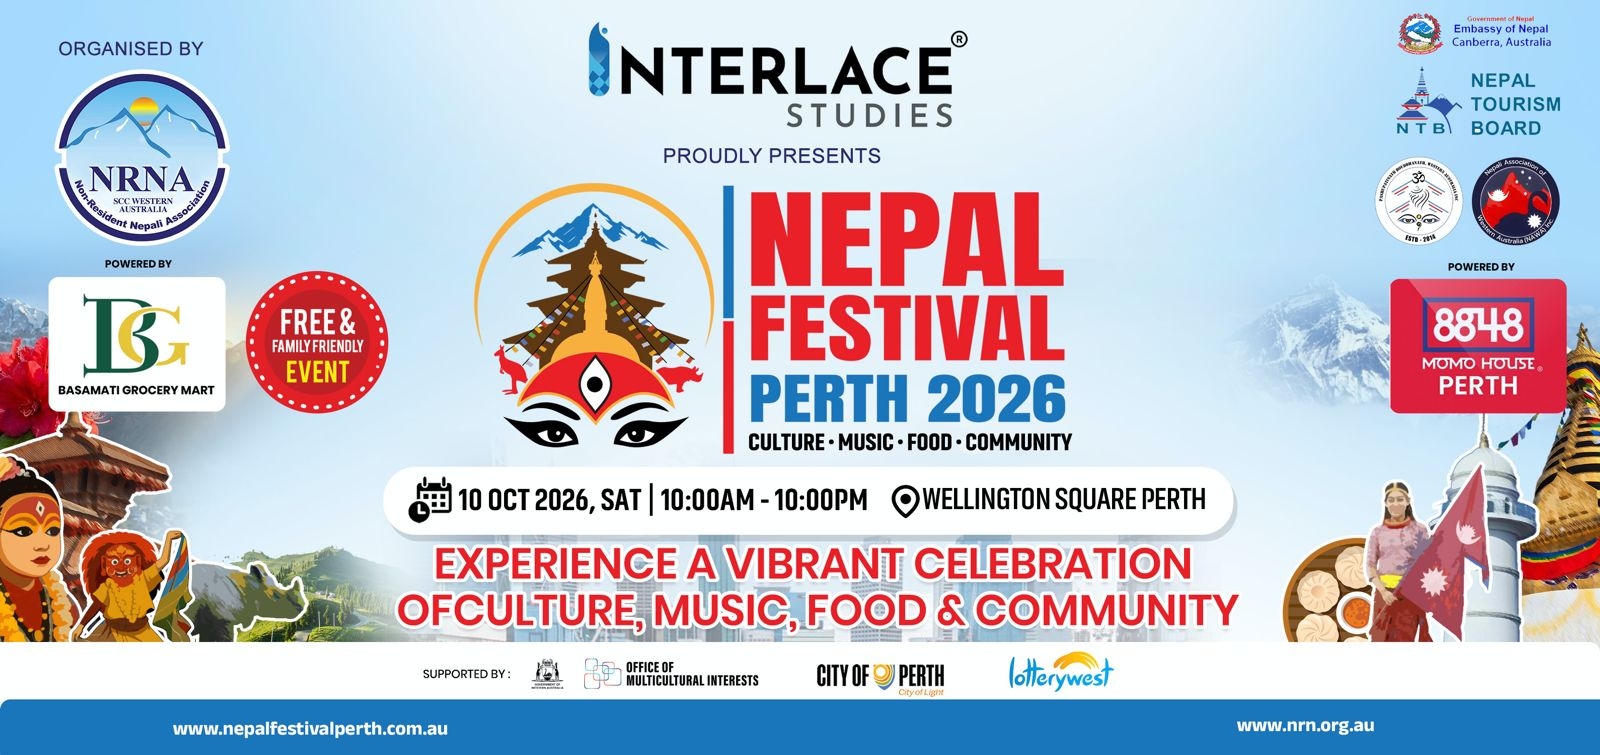 Nepal Festival Perth 2026 FestivalOct 10, 2026 10:00 AM · Perth / Western Australia · 220 views
-
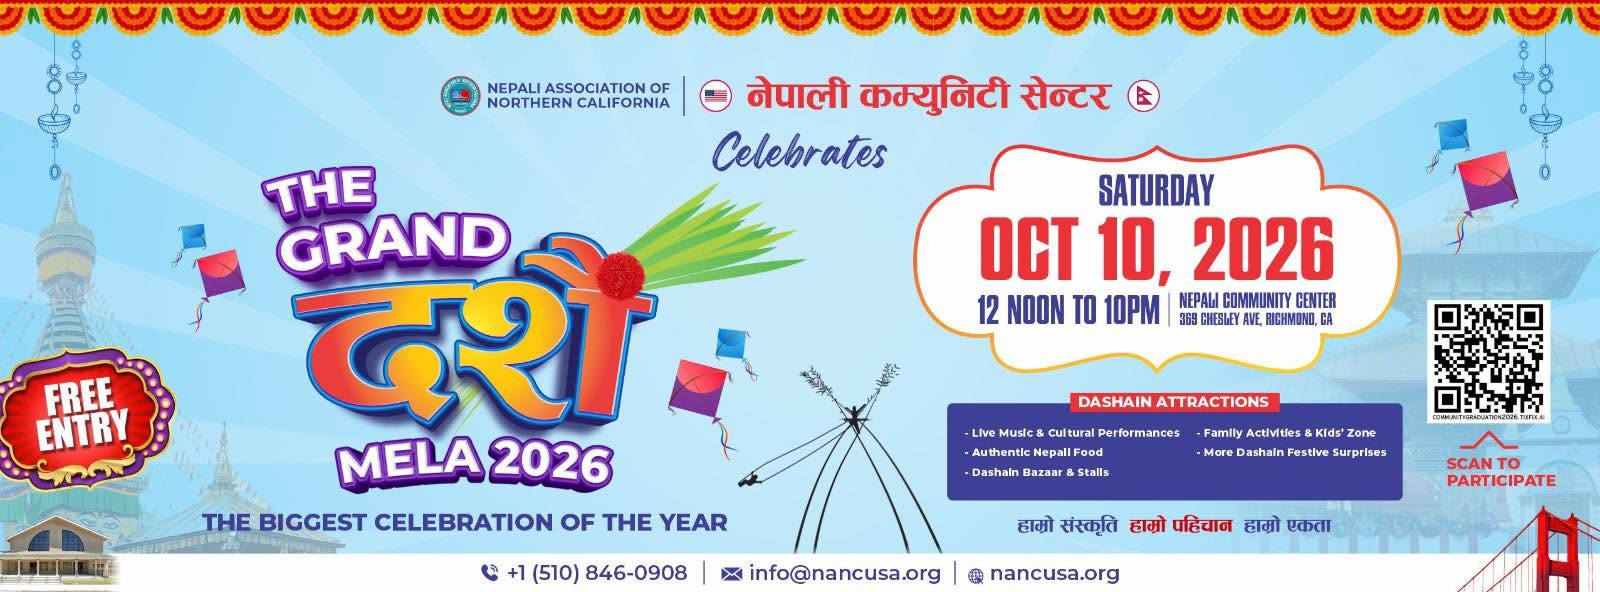 Grand Dashain Mela 2026 FestivalOct 10, 2026 11:00 AM · Bay Area / Northern California · 209 views
-
 Oct 11, 2026 11:00 AM · DMV / Greater Washington · 221 views · Dashain
-
 Dashain Festival Fulpati PartyOct 17, 2026 10:00 PM · Greater London · 183 views · Dashain
-
✓Vianet Communications OtherKathmandu · · 280 views
-
Aama Lama RestaurantMalden, MA · · 238 views
-
Ailaa Himalayan Bar & Grill RestaurantStoneham, MA · · 239 views
-
Ailaa Himalayan Bar & Grill RestaurantBedford, TX · · 214 views
-
Annapurna Curry & Sekuwa House RestaurantManchester, NH · · 218 views